Regulatory Alert | Financial Services | Cyber & Operational Resilience
Executive Summary
On 7 July 2026, the ECB's Supervisory Board issued a letter to all significant institutions under the SSM addressing the accelerating impact of frontier AI on the cyber threat landscape. Institutions must submit a comprehensive action plan to their Joint Supervisory Team by 31 October 2026. We summarise the requirements, our point of view, and a related but distinct post-quantum cryptography signal that should not be conflated with the current mandate.
The Regulatory Ask
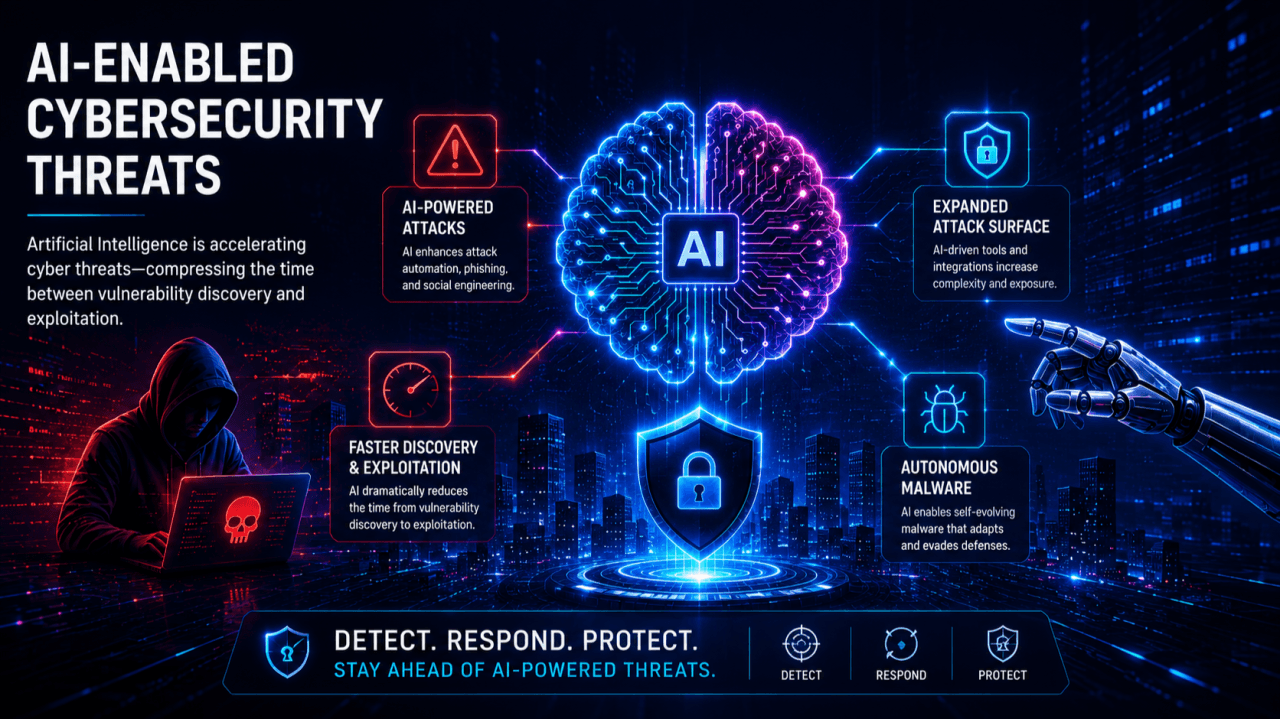
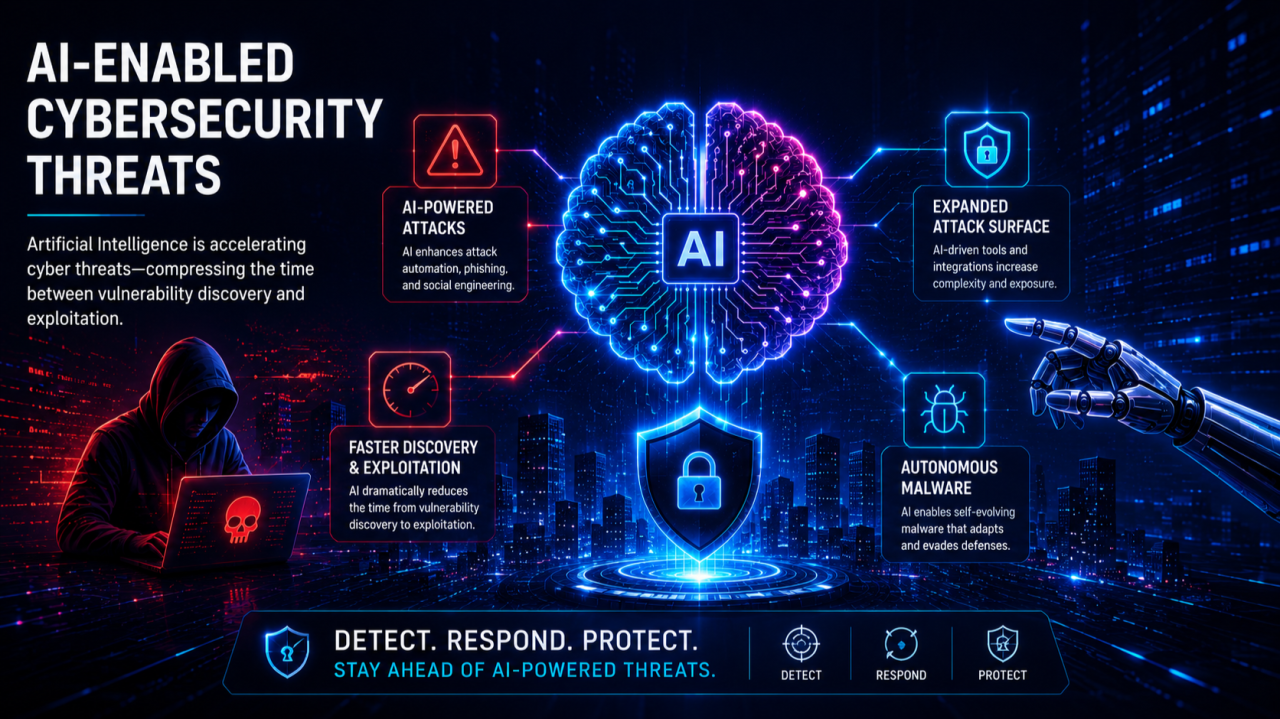
The ECB's position is measured: AI does not introduce new risk categories, but compresses the timeline between vulnerability discovery and exploitation. This reframes existing DORA obligations around resourcing and response speed. Action plans must address six areas: attack surface prioritisation (including third-party and open-source asset identification); accelerated, AI-assisted vulnerability and patch management with human oversight; enhanced monitoring and detection; governance, funding and supply chain assurance; defence-in-depth modernisation; and operational resilience, including tested crisis management. Notably, the ECB extended the IT Risk Questionnaire deadline from September 2026 to February 2027, signalling where supervisory priority sits this cycle.
Our Point of View
For institutions with mature DORA programmes, this is an acceleration mandate, not a net-new requirement. The critical path is demonstrating operational capacity — staffing, tooling, governance cadence — to execute existing controls faster. The October submission will likely be scrutinised on this dimension specifically.
A Distinct Consideration: Post-Quantum Cryptography
The letter briefly flags that quantum computing's threat to traditional encryption will be addressed in a separate, forthcoming letter, and states PQC adoption "must start now." It contains no reference to cryptographic asset inventories, algorithm agility, or PQC standards, and the October action plan is not scoped to cryptographic risk. We would caution against framing PQC readiness as a response to this letter.
There is, however, a defensible operational parallel: the asset discovery and risk appetite updates required under this letter rely on the same discipline as cryptographic asset discovery (e.g., a Cryptographic Bill of Materials) — systematic inventory, ownership, prioritisation and remediation tracking, applied to a different asset class. Institutions may find it efficient to scope discovery capability broadly enough to extend to cryptographic assets ahead of the ECB's forthcoming PQC letter. This is a capability-reuse argument, not a claim about this letter's regulatory scope.
Recommended Next Steps
- Assess action plan readiness against the six focus areas in Annex 1
- Confirm governance ownership for the 31 October 2026 submission
- Evaluate whether ICT asset discovery capability can be architected for extensibility to cryptographic assets
- Monitor for publication of the ECB's forthcoming letter on quantum computing and post-quantum cryptography
Source
ECB Letter SSM-2026-0301, 7 July 2026, bankingsupervision.europa.eu.