Regulatory Compliance
13 articles
APRA, ASD, and the Cryptographic Inventory Problem
APRA's sharpened focus on quantum computing risk lines up with ASD guidance calling for a PQC transition plan by end of 2026 — but a credible plan starts with a cryptographic inventory most regulated entities don't yet have.
Read Article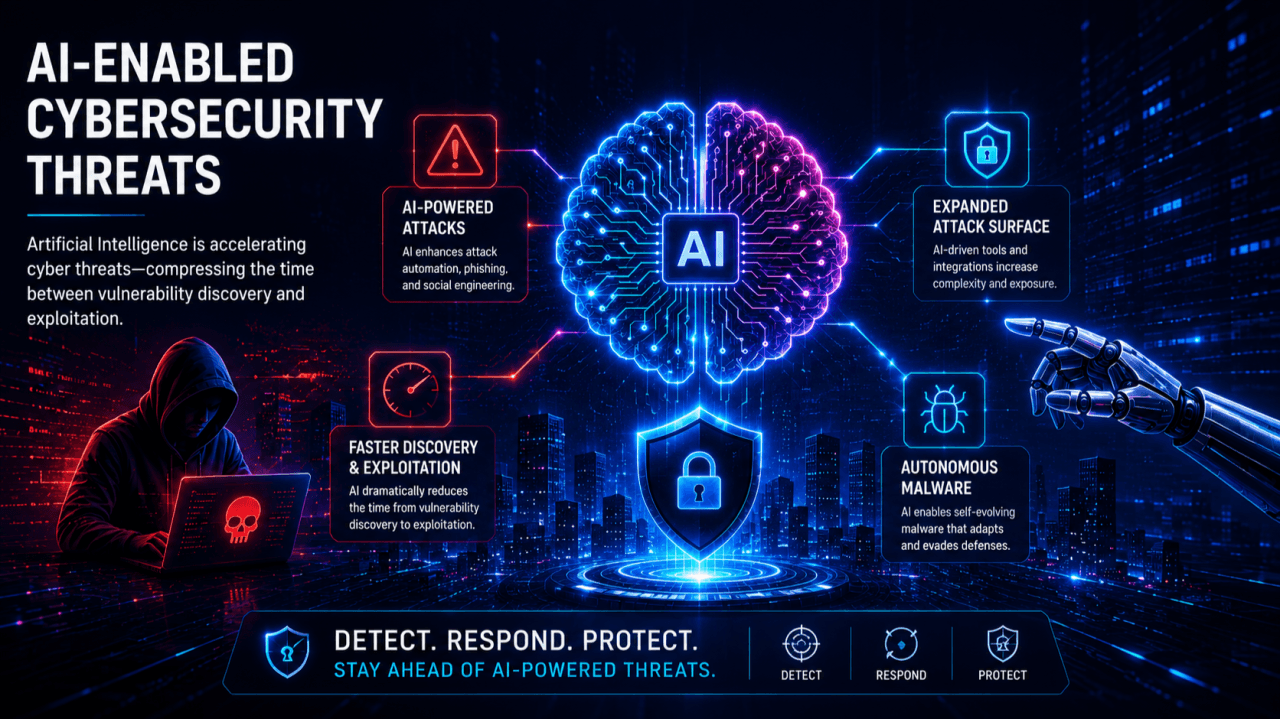
AI-Enabled Cybersecurity Threats: What the ECB's Letter Means for Significant Institutions
The ECB's Supervisory Board has ordered SSM-significant institutions to submit an AI-cyber-threat action plan by 31 October 2026 — and flagged a separate, forthcoming letter on post-quantum cryptography.
Read Article
The CISA PQC Playbook: Official Guidance on Technologies Ready for Upgrade
CISA has published official guidance on which technology categories are ready for post-quantum migration, following Executive Order 14306. Here's what belongs in your 2026 procurement policy.
Read Article
Data Shelf Life and System Lifecycle in Banking & Financial Services
SEC, FINRA, and MiFID II mandate 3-7 years of tamper-evident record retention in banking. That same window is exactly the exposure period Harvest-Now-Decrypt-Later attacks are built to exploit.
Read Article
Data Shelf Life and System Lifecycle in Digital Healthcare
UK and US rules keep health records for anywhere from 6 to 25+ years. For genomic data, imaging, and clinical notes, that's a multi-decade window sitting exposed to Harvest-Now-Decrypt-Later attacks.
Read Article
Quantum Threat Modeling: Preparing SMEs for the Future of Cybersecurity
Small and medium-sized enterprises often assume quantum risk is a problem for tech giants. But SMEs sit inside larger supply chains, making them appealing targets — and most still rely on legacy infrastructure and external vendors for cybersecurity.
Read Article
The Critical Role of AI Governance in Shaping Our Technological Future
As AI safety institutes launch across the US, UK, Singapore, and Japan and the EU AI Office takes shape, robust governance frameworks are becoming the cornerstone of responsible AI integration — with quantum cybersecurity governance next on the horizon.
Read Article
The Vital Role of Cryptography in Our Digital World
Confidentiality, authentication, and legal history all depend on cryptography holding up against quantum attackers. A summary of Jaime Gómez García's IIF Quantum Bootcamp talk, and what it means for regulated migration timelines.
Read Article
Overview of the DORA Regulation (Digital Operational Resilience Act)
DORA is an EU-wide regulation designed to strengthen cybersecurity and operational resilience across the financial sector, becoming legally binding on January 17, 2025.
Read Article
The EU Cyber Resilience Act: A C-Suite Guide to Future-Proofing Your Digital Products
The EU Cyber Resilience Act (CRA) is reshaping how digital products are built, supported, and documented for the EU market. Here's what C-level executives need to know to prepare.
Read Article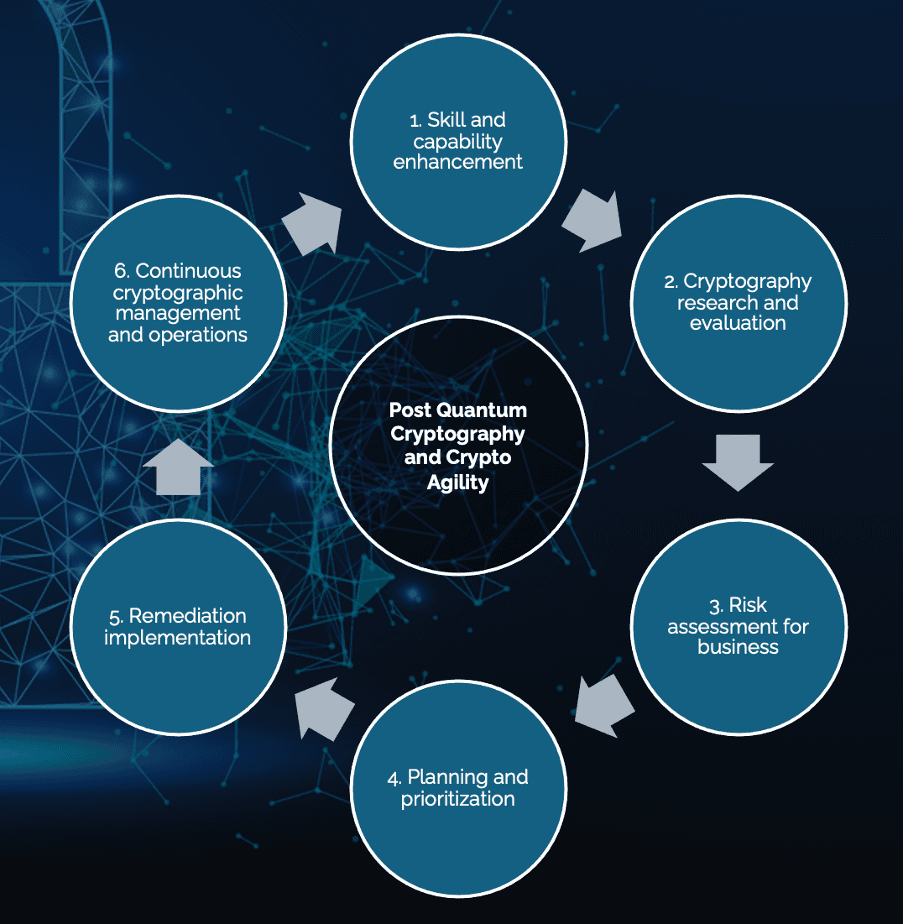
Quantum Cybersecurity Governance, Risk and Compliance (GRC): What Could Be a Starting Point?
A six-phase framework for organizations beginning their transition to crypto-agility and Post-Quantum Cryptography, with governance underpinning every stage.
Read Article
Quantum Cybersecurity Compliance: Ensuring Cybersecurity in the Age of Quantum Computing
A global tour of post-quantum regulation and standardization — from NIST and ETSI to China's quantum communication backbone — and what it means for organizations planning their transition.
Read Article
The Future of Cybersecurity in Financial Services: Steering the Ship Through Quantum Seas
Based on the recent UK Finance report — the key quantum cybersecurity risks facing the financial sector, and how major UK banks are already getting ahead of them.
Read Article