Harvest Now Decrypt Later
28 articles
APRA, ASD, and the Cryptographic Inventory Problem
APRA's sharpened focus on quantum computing risk lines up with ASD guidance calling for a PQC transition plan by end of 2026 — but a credible plan starts with a cryptographic inventory most regulated entities don't yet have.
Read Article
The Blueprint Problem: What the Shell and Philips Breach Reveals About Cryptographic Hygiene
Cl0p breached nearly fifty organizations, including Shell and Philips, through a single vulnerability in PTC's Windchill platform. The patch closes the entry point — it doesn't answer what protected the data once it left.
Read Article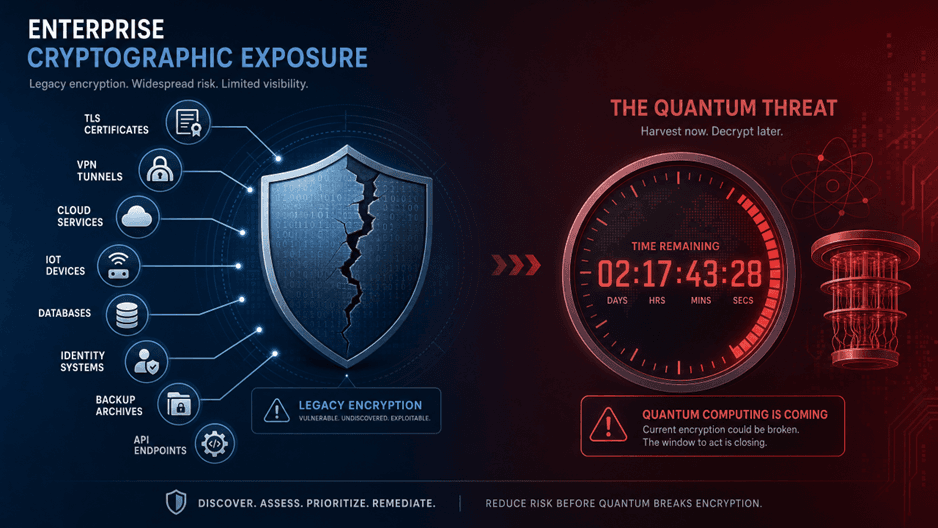
The Dangerous Illusion: Why Claude Mythos Cannot Solve Your Cryptographic Inventory Problem
Frontier AI is compressing exploit timelines, but it cannot map a sprawling cryptographic estate. Quantum safety remains a governance and inventory challenge, not a modeling problem.
Read Article
Vendors Are Not Your Quantum Safety Net: The $3.3 Trillion Accountability Gap US Boardrooms Can No Longer Ignore
62% of executives are waiting for vendors to make them quantum-safe. With Fedwire disruption risk alone estimated at $2-3.3 trillion, that wait is the biggest unmanaged risk in the room.
Read Article
The CISA PQC Playbook: Official Guidance on Technologies Ready for Upgrade
CISA has published official guidance on which technology categories are ready for post-quantum migration, following Executive Order 14306. Here's what belongs in your 2026 procurement policy.
Read Article
The Quantum Underground: Hacker Chatter and What It Means for Cybersecurity
Threat actors aren't waiting for a firm 'Q-day.' Europol and UK NCSC guidance now frame harvest-now-decrypt-later as an active risk vector, with concrete deadlines already in force.
Read Article
Drones Are Using Yesterday's Locks on Tomorrow's Threats: The Quantum Encryption Emergency
UAVs rely on RSA and ECC to secure command links and firmware signing — both breakable by a cryptographically relevant quantum computer. A harvest-now-decrypt-later and sign-today-forge-tomorrow risk case study.
Read Article
JLR's Breach: A Wake-Up Call for Quantum-Ready Security
The September 2025 Jaguar Land Rover cyberattack halted production and threatened 100,000 UK jobs. It wasn't a quantum attack — but it's a preview of what Harvest Now, Decrypt Later makes possible.
Read Article
OT Security Insights: Securing Critical Infrastructure in the Quantum Era
Operational technology systems can run for decades — making them uniquely exposed to harvest-now-decrypt-later attacks. An OT-specific checklist for the post-quantum transition.
Read Article
Data Shelf Life and System Lifecycle in Banking & Financial Services
SEC, FINRA, and MiFID II mandate 3-7 years of tamper-evident record retention in banking. That same window is exactly the exposure period Harvest-Now-Decrypt-Later attacks are built to exploit.
Read Article
Data Shelf Life and System Lifecycle in Digital Healthcare
UK and US rules keep health records for anywhere from 6 to 25+ years. For genomic data, imaging, and clinical notes, that's a multi-decade window sitting exposed to Harvest-Now-Decrypt-Later attacks.
Read Article
Inside the Quantum Attack Toolkit: Real-World Threats and Data Risks
Shor's algorithm, Grover's algorithm, side-channel exploits, crosstalk attacks, and Harvest-Now-Decrypt-Later — the offensive quantum toolkit is moving from theoretical to practical faster than most businesses realize.
Read Article
Securing Supply Chains in the Quantum Era: Risk Assessment, Resilience & Readiness
Quantum computers threaten to render today's TLS, blockchain provenance, and access-token cryptography obsolete. Quantum Risk Assessment is the emerging practice for finding exposure before adversaries do.
Read Article
Quantum Risk & Timeline Report: A Strategic Brief for CISOs, SOC Leaders, and Risk Teams
Consolidating the latest public intelligence from NIST, FBI, NSA, MITRE, and DHS/CISA into a quantum threat timeline, key risk categories, and five recommendations for proactive security leaders.
Read Article
Quantum-Ready SOC: Preparing for a Post-Quantum Cybersecurity Era
NIST estimates the first quantum breaches may occur as soon as 2030. Security Operations Centers excel at real-time incidents, but quantum risk is a long-tail, high-impact category most SOCs aren't yet built to handle.
Read Article
Quantum Malware and the Boardroom Blind Spot: Preparing for Invisible Threats
There are currently no quantum intrusion detection systems, no forensic methods to inspect qubit histories, and no baseline behavioral models for quantum workloads. Board members can't detect what they can't see coming.
Read Article
The Human Factor of Quantum: Understanding the Role of People in Quantum Security
Quantum-resistant encryption and post-quantum cryptographic measures can be undermined by simple human mistakes. The path to quantum resilience is paved not just by technology, but by people.
Read Article
Quantum Threat Modeling: Preparing SMEs for the Future of Cybersecurity
Small and medium-sized enterprises often assume quantum risk is a problem for tech giants. But SMEs sit inside larger supply chains, making them appealing targets — and most still rely on legacy infrastructure and external vendors for cybersecurity.
Read Article
Quantum and Maritime Security: Navigating the Future with Quantum Safety
The 2017 NotPetya attack on Maersk cost up to $300 million and showed how dependent maritime operations are on digital infrastructure. Quantum computing threatens to undermine the encryption protecting that infrastructure next.
Read Article
The Vital Role of Cryptography in Our Digital World
Confidentiality, authentication, and legal history all depend on cryptography holding up against quantum attackers. A summary of Jaime Gómez García's IIF Quantum Bootcamp talk, and what it means for regulated migration timelines.
Read Article
The Quantum Countdown: Why Your Organization's Cybersecurity Future Starts Today
A deep dive into the post-quantum cryptography revolution: the harvest-now-decrypt-later threat is already in motion, and Mosca's Theorem shows why the window to act is now, not later.
Read Article
Post-Quantum Cryptography Takes Center Stage: This Week's Breakthroughs
NIST's new quantum-resistant standards have arrived, tech giants are racing to implement them, and Australia just joined the billion-dollar quantum club. Here's what happened this week.
Read Article
Quantum Leap: Moving from Digital to Quantum Transformation
The U.S. government's Federal Quantum Action Plan lays out a four-principle roadmap for migrating federal systems to post-quantum cryptography — and a $7.1 billion price tag to match.
Read Article
Quantum Cybersecurity Risk Assessment in Banking — In Practice
How a bank began its quantum cybersecurity journey, what motivated the assessment, and how Cystel's four-pronged approach uncovered real gaps in the institution's cryptographic posture.
Read Article
The White House "Report on Post-Quantum Cryptography"
The White House's Report on Post-Quantum Cryptography lays out the U.S. national strategy for transitioning to PQC, including a $7.1 billion cost estimate and a prioritized migration plan.
Read Article
The Future of Cybersecurity in Financial Services: Steering the Ship Through Quantum Seas
Based on the recent UK Finance report — the key quantum cybersecurity risks facing the financial sector, and how major UK banks are already getting ahead of them.
Read Article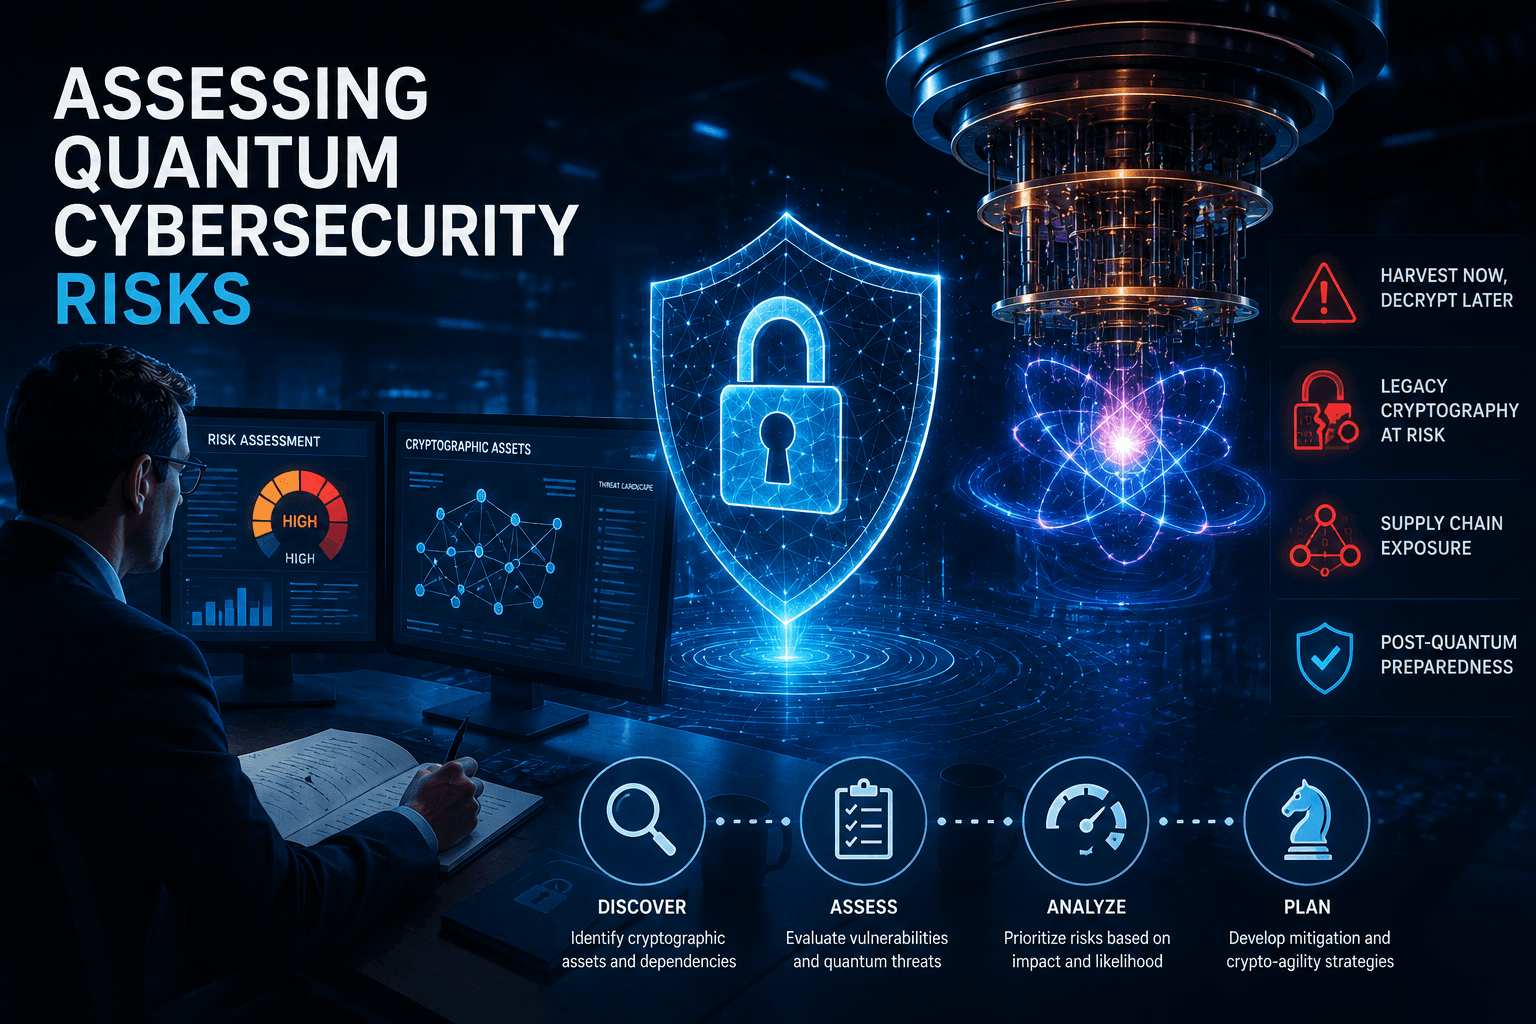
Assessing Quantum Cybersecurity Risks: An Introduction to Navigating the New Threat Landscape
How Cryptographically Relevant Quantum Computers reshape risk assessment — the anatomy of a Quantum Cryptanalytic Risk Assessment (QCRA), and a real-world crypto-agility risk model.
Read Article
Is the Quantum Cybersecurity Threat Already a Reality?
What experts predict about the timeline to a cryptographically relevant quantum computer, and what Hudson Institute research suggests a quantum attack could cost the US financial system.
Read Article